Downloads instruction file steered coding agent, firm says
Forever Security says it blocked a customer coding agent's malicious package install attempt and then demonstrated separate Codex and Claude Code instruction-file attacks. The customer file's arrival route and tested agent versions remain unknown.
The big change
What changed: A coding agent can treat a downloaded instruction file as a request to change its own configuration, extending the file's influence beyond Downloads. Forever observed a blocked customer attempt and demonstrated that path under controlled conditions.
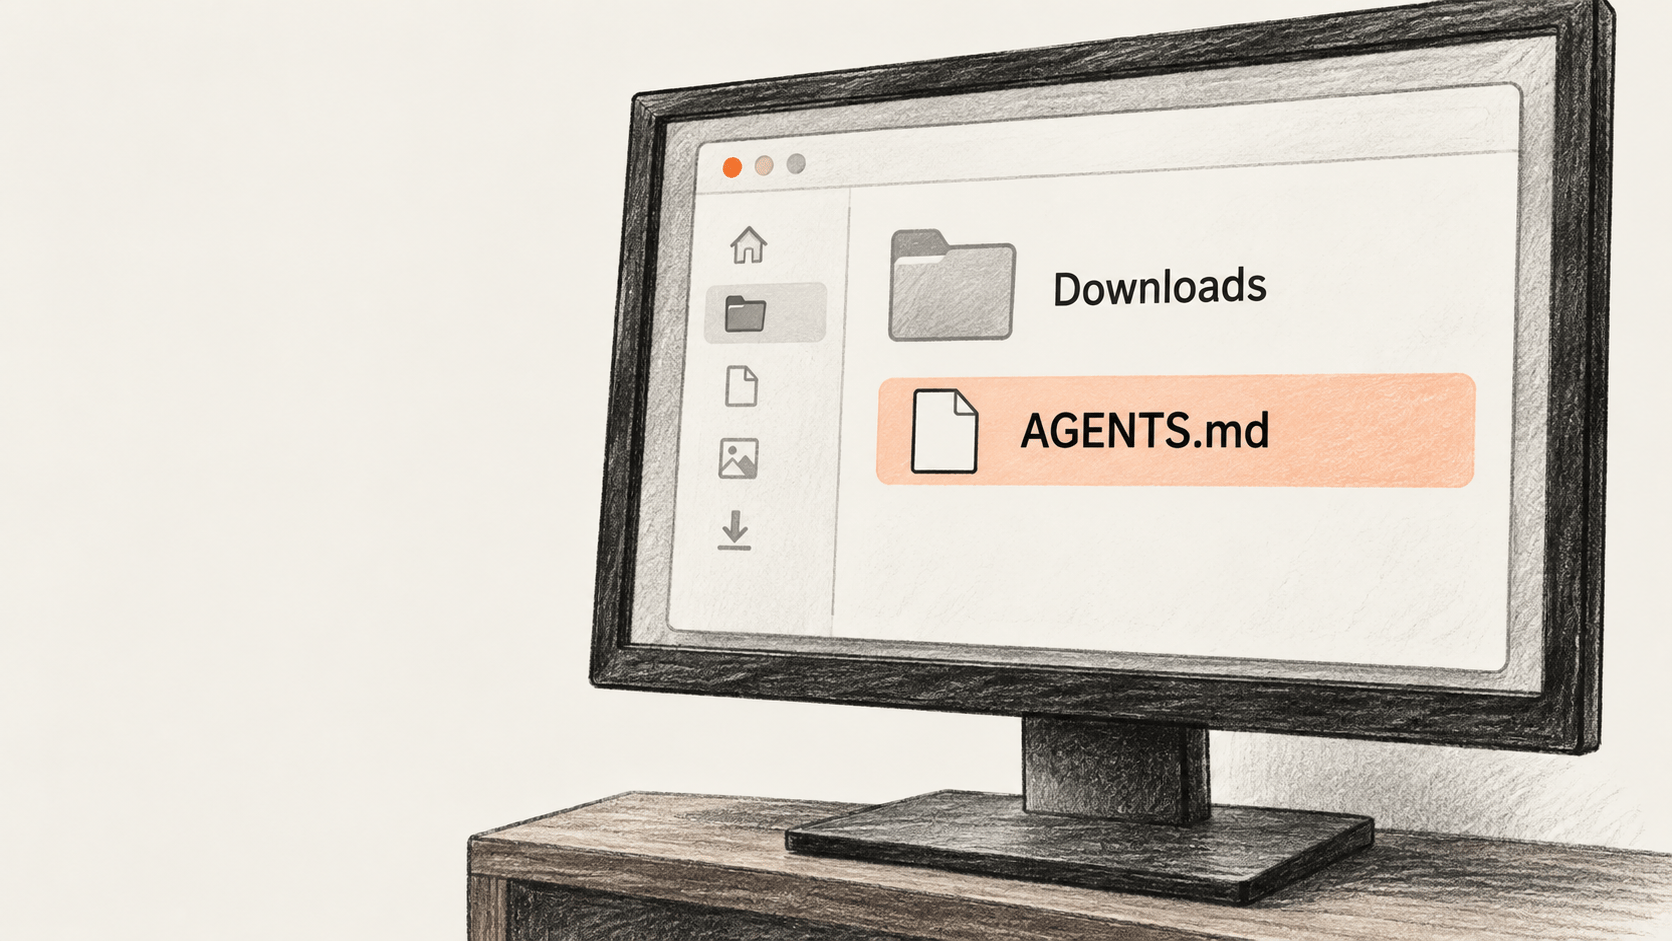
Why it matters: A folder used for browser downloads can also become a coding agent's working directory. In that setting, attacker-controlled text may be presented as project guidance and can request changes beyond the downloaded file.
What to watch: The report does not identify affected agent versions or provide test counts behind its success rates. Whether an attempted action runs depends on the agent's instruction loading, workspace trust, permissions, sandbox and the user's decisions.